The Role of Thales Key Management in Modern Enterprise Security Architecture
05 Oct, 2026
11 Views 0 Like(s)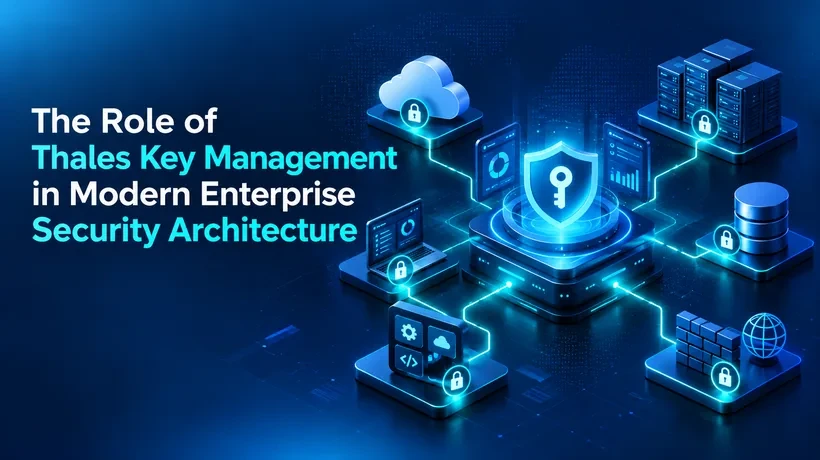
Modern enterprise security architectures depend on encryption, authentication, digital certificates, and other cryptographic controls to protect critical information. Thales key management can help organizations establish centralized control over the cryptographic keys that support these security technologies. When integrated with effective Key management and key management in cryptography practices, centralized key control can strengthen enterprise security architecture.
Introduction
Modern enterprise IT environments have become increasingly distributed.
Organizations use cloud platforms, on-premises infrastructure, SaaS applications, databases, APIs, mobile services, and digital identity systems to support business operations.
These technologies depend on cryptography.
Businesses use encryption to protect information, digital signatures to establish authenticity, and cryptographic keys to support authentication and secure communications.
As infrastructure expands, organizations may manage large numbers of cryptographic keys across multiple systems.
This creates a need for centralized control.
Thales key management can support organizations that need structured management of cryptographic keys across modern enterprise environments.
When integrated with effective Key management and key management in cryptography practices, centralized key management can become an important component of enterprise security architecture.
Understanding Modern Enterprise Security Architecture
Enterprise security architecture includes the technologies, processes, policies, and controls organizations use to protect digital assets.
A modern architecture may include:
-
Identity and access management
-
Network security
-
Application security
-
Data security
-
Cloud security
-
Endpoint security
-
Encryption
-
Monitoring
-
Incident response
Cryptographic security supports many of these areas.
Why Cryptographic Keys Matter
Cryptographic keys support:
-
Data encryption
-
Authentication
-
Digital signatures
-
Certificates
-
Secure communications
-
Application security
These keys can become critical security assets.
Organizations must therefore manage them carefully.
Key Management in Cryptography
Key management in cryptography provides a framework for controlling keys throughout their lifecycle.
The lifecycle includes:
-
Generation
-
Storage
-
Distribution
-
Access
-
Usage
-
Rotation
-
Backup
-
Recovery
-
Retirement
-
Destruction
Organizations should integrate these processes into their broader security architecture.
Centralized Key Management
Centralized Key management provides a structured approach to controlling cryptographic assets across different systems.
Instead of allowing every application or infrastructure team to manage keys independently, organizations can establish common policies.
Centralization can improve:
-
Visibility
-
Governance
-
Access control
-
Lifecycle management
-
Rotation
-
Monitoring
The Role of Thales Key Management
Thales key management can support centralized administration of cryptographic keys across enterprise environments.
Organizations can use centralized capabilities to manage key-related activities across:
-
Applications
-
Databases
-
Cloud environments
-
On-premises infrastructure
-
Enterprise services
This can help security teams establish a more consistent cryptographic security framework.
Cloud Security Architecture
Cloud computing introduces additional requirements for cryptographic security.
Organizations may use several cloud providers or combine cloud and on-premises infrastructure.
This can distribute encryption keys across different environments.
Centralized Key management can help organizations establish common policies for these environments.
Database Security
Enterprise databases often contain sensitive information.
Organizations may use encryption to protect database records.
The associated cryptographic keys require protection.
Centralized Key management can provide structured control over database encryption keys and their lifecycle.
Application Security
Enterprise applications often use cryptographic keys for:
-
Encryption
-
Authentication
-
API security
-
Digital signatures
Applications should not store sensitive keys unnecessarily within their own code or configuration.
Centralized Key management can provide applications with controlled access to required cryptographic functions.
Identity and Authentication
Cryptographic keys also support enterprise identity systems.
Certificates and private keys can establish trusted identities for users, services, and applications.
Organizations should manage these assets throughout their lifecycle.
Digital Signatures
Digital signatures help organizations verify the authenticity and integrity of digital information.
Private signing keys require strong protection.
Centralized Key management can help organizations control access and lifecycle policies around signing keys.
Monitoring and Governance
Security architecture requires visibility.
Organizations should monitor cryptographic activity, including:
-
Key access
-
Key creation
-
Key rotation
-
Administrative changes
-
Failed access attempts
-
Key retirement
Monitoring can support security operations and governance.
Key Management and Security Policies
Organizations should establish formal Key management policies.
Policies should address:
-
Key ownership
-
Approved cryptographic technologies
-
Key generation
-
Key storage
-
Access control
-
Rotation
-
Backup
-
Recovery
-
Retirement
These policies should integrate with wider enterprise security policies.
Managing Cryptographic Risk
Organizations can reduce cryptographic risk by:
-
Maintaining a complete key inventory
-
Separating keys from protected data
-
Applying least privilege
-
Rotating keys appropriately
-
Monitoring activity
-
Retiring obsolete keys
-
Testing recovery procedures
Centralized Key management can help coordinate these practices.
Common Challenges
Distributed Infrastructure
Multiple cloud and on-premises environments can fragment Key management.
Key Sprawl
Organizations may accumulate large numbers of cryptographic keys.
Inconsistent Policies
Different teams may manage keys differently.
Legacy Systems
Older applications may create integration challenges.
Limited Visibility
Security teams may struggle to identify every cryptographic asset.
Best Practices for Enterprise Architecture
Establish Centralized Control
Create a common framework for managing cryptographic keys.
Assign Ownership
Every critical key should have a clearly defined owner.
Apply Least Privilege
Limit access to authorized users and applications.
Automate Lifecycle Management
Automate routine rotation and monitoring where appropriate.
Monitor Activity
Review cryptographic events regularly.
Test Recovery
Ensure that authorized teams can recover critical keys.
Retire Obsolete Assets
Remove unnecessary keys according to established procedures.
Conclusion
Cryptography forms an important part of modern enterprise security architecture.
Organizations rely on encryption, authentication, digital certificates, digital signatures, and secure communications to protect business information.
These technologies depend on cryptographic keys, making effective Key management essential.
Key management in cryptography provides the framework for managing keys throughout their lifecycle, while centralized Key management helps organizations maintain consistent policies and greater visibility.
Thales key management can support centralized control across applications, databases, cloud platforms, and other enterprise environments.
By integrating centralized key management into the wider security architecture, organizations can improve cryptographic governance, strengthen access control, manage key lifecycles more effectively, and establish a more structured approach to protecting critical digital assets.
Comments
Login to Comment