How Key Management in Cryptography Supports Secure Backup and Disaster Recovery
15 Oct, 2026
13 Views 0 Like(s)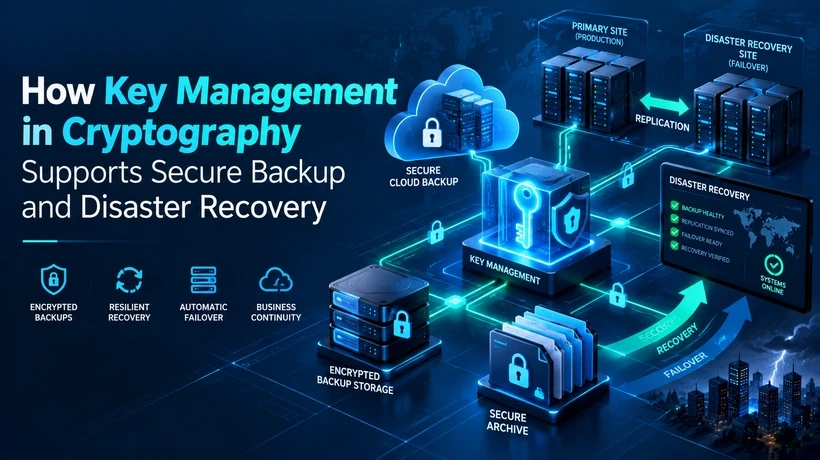
Backup and disaster recovery strategies protect organizations against data loss, system failures, and disruptive security incidents. Key management in cryptography ensures that the keys required to access encrypted backups remain protected, available, and properly controlled.
Introduction
Backup and disaster recovery have become essential components of enterprise resilience.
Organizations create backups to protect business information against accidental deletion, hardware failures, application problems, cyber incidents, and other disruptions.
Businesses increasingly encrypt backup data to prevent unauthorized access.
However, encrypted backups depend on cryptographic keys.
If an organization protects its backup files but loses the keys required to decrypt them, the backups may become inaccessible to authorized users.
This makes Key management an important part of backup and disaster recovery planning.
A strong approach to key management in cryptography helps organizations protect encryption keys while ensuring that authorized teams can recover them when necessary.
Why Backups Need Encryption
Backup environments can contain large amounts of sensitive information.
A single backup may include:
-
Customer records
-
Financial information
-
Employee data
-
Application databases
-
Business documents
-
System configurations
If attackers gain access to unprotected backups, they may obtain sensitive information.
Encryption can provide an additional layer of protection.
However, organizations must also protect the keys used to encrypt and decrypt those backups.
The Role of Key Management in Cryptography
Key management in cryptography covers the complete lifecycle of cryptographic keys.
The lifecycle generally includes:
-
Generation
-
Storage
-
Distribution
-
Access
-
Usage
-
Rotation
-
Backup
-
Recovery
-
Retirement
-
Destruction
Backup and disaster recovery strategies should account for each of these stages.
Protecting Backup Encryption Keys
Organizations should avoid storing encryption keys in the same location as encrypted backups when doing so would create unnecessary exposure.
A compromise of both the backup and its key could undermine the protection provided by encryption.
Security teams should establish appropriate separation between backup data and cryptographic key infrastructure.
Availability and Security Must Work Together
Key management for disaster recovery presents an important balance.
Keys must remain highly protected, but authorized personnel must also be able to recover them during an emergency.
If security controls make keys completely inaccessible during a disaster, recovery operations may fail.
Organizations should therefore design recovery procedures that provide controlled access to critical keys.
Key Backup and Key Data Backup Are Different
Organizations often focus on backing up business data.
However, cryptographic keys also require secure backup and recovery planning.
A backup strategy should identify:
-
Which keys are critical
-
Where key backups are stored
-
Who can access them
-
How recovery is authorized
-
How recovery is tested
Key backups should receive appropriate protection.
Disaster Recovery Planning
A disaster recovery plan should include cryptographic dependencies.
For every critical application, organizations should understand:
-
Which data requires encryption
-
Which keys protect that data
-
Where those keys reside
-
Which applications require access
-
How keys will be recovered
This information can prevent delays during an actual recovery event.
Key Recovery Procedures
Organizations should document the steps required to recover cryptographic keys.
A recovery process may involve:
-
Confirming the recovery event
-
Authenticating authorized personnel
-
Retrieving the appropriate key backup
-
Restoring the key through approved procedures
-
Verifying key availability
-
Restoring dependent applications
-
Recording the recovery activity
Organizations should test this process regularly.
Testing Key Recovery
A disaster recovery plan is only useful if it works in practice.
Organizations should conduct recovery exercises to verify that:
-
Key backups are available
-
Recovery personnel know the procedure
-
Applications can access restored keys
-
Permissions work correctly
-
Recovery takes an acceptable amount of time
Testing can reveal gaps before a real incident occurs.
Key Rotation and Backups
Key rotation can create additional considerations for backup environments.
An organization may rotate an active encryption key while older backups still depend on previous keys.
Security teams should retain historical keys according to documented policies when authorized recovery of older backups requires them.
At the same time, organizations should avoid keeping unnecessary keys indefinitely.
Managing Retired Keys
A key should not automatically remain active forever simply because an old backup exists.
Organizations should establish retention policies that consider:
-
Backup retention periods
-
Legal requirements
-
Business requirements
-
Security policies
Once protected data reaches the end of its required retention period, associated keys can be reviewed for appropriate retirement.
Protecting Cloud Backups
Many organizations use cloud storage for backup and disaster recovery.
Cloud backup environments can involve multiple services and geographic locations.
Security teams should understand:
-
Where backup data resides
-
Which keys protect it
-
Who can access those keys
-
How recovery works
-
How keys are backed up
Centralized Key management can help maintain consistent policies.
Hybrid Disaster Recovery
Some organizations use hybrid recovery models.
For example, a business may operate production systems on-premises while storing backup data in the cloud.
During a disruption, workloads may move to another environment.
Cryptographic keys must remain available to authorized recovery systems.
This makes Key management an important component of hybrid disaster recovery architecture.
Least Privilege During Recovery
Emergency situations can create pressure to grant broad access.
However, organizations should maintain appropriate access controls even during recovery.
Only authorized personnel and systems should access sensitive cryptographic keys.
Temporary permissions should be reviewed and removed after recovery operations conclude.
Monitoring Key Recovery
Key recovery activities should generate appropriate audit records.
Organizations should monitor:
-
Key recovery
-
Administrative changes
-
Key access
-
Failed recovery attempts
-
Permission changes
These records can help security teams investigate unusual activity.
Protecting Against Ransomware
Encrypted backups can help organizations recover from disruptive incidents.
However, attackers may attempt to access or destroy backup infrastructure.
Organizations should therefore protect both backup data and the cryptographic keys associated with it.
Access to backup and Key management systems should receive strong controls.
Common Key Management Challenges
Lost Keys
Organizations may lose access to critical encrypted backups.
Poor Documentation
Recovery teams may not know which keys support specific backups.
Excessive Access
Too many administrators may have recovery permissions.
Untested Recovery
Organizations may assume that recovery works without testing it.
Key Sprawl
Old keys may accumulate without proper lifecycle management.
Best Practices
Organizations should:
-
Inventory keys associated with critical backups.
-
Separate keys from encrypted backup data.
-
Protect key backups.
-
Restrict recovery access.
-
Document recovery procedures.
-
Test recovery regularly.
-
Track key dependencies.
-
Maintain appropriate historical keys for required backup retention.
-
Monitor recovery activity.
-
Review obsolete keys regularly.
-
Integrate Key management with disaster recovery planning.
-
Test application access after key recovery.
Conclusion
Backup and disaster recovery strategies depend on both data availability and cryptographic availability.
Organizations may successfully restore encrypted data but still face recovery problems if they cannot access the associated cryptographic keys.
Key management in cryptography provides the framework for securely generating, storing, accessing, backing up, recovering, rotating, and retiring keys.
Effective Key management allows businesses to protect encrypted backups while maintaining controlled access during disaster recovery.
By integrating cryptographic key management into business continuity and disaster recovery planning, organizations can improve resilience without compromising the security of their sensitive information.
Comments
Login to Comment